What visitors may see: the Anonymous role
This page is for website creators who decide what the public can see and do. A visitor who is not logged in is the Anonymous user, and everything they may do comes from the roles assigned to it.
Contents
- The Anonymous user and role
- What it grants by default
- Siteaccess settings
- Giving visitors more
- Testing as a visitor
- Common mistakes
The Anonymous user and role
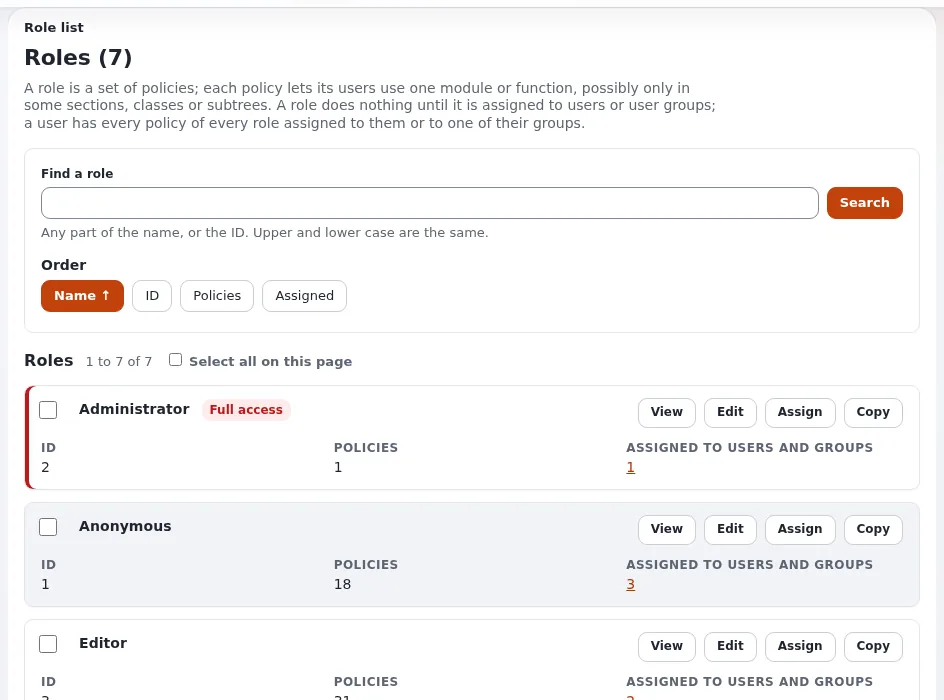
Every request without a login runs as the Anonymous user, a member of the Anonymous user group. Its permissions come from the role assigned to that group, usually called Anonymous (Roles and policies).
What it grants by default
The default Anonymous role has content/read and content/pdf limited to Section Standard. That one limitation keeps
user accounts, the media library's own pages, setup objects and every other section away from visitors
(Sections). It also has user/login for the public siteaccesses.
Siteaccess settings
site.ini [SiteAccessSettings]:
| Key | Meaning |
|---|---|
RequireUserLogin | true in site.ini; a public siteaccess sets false. true sends every visitor to the login page |
AnonymousAccessList[] | module views reachable without login even with RequireUserLogin=true (user/register, user/success, user/activate, user/forgotpassword, csp/report ...) |
Giving visitors more
| Visitors should | Add to the Anonymous role |
|---|---|
| Read a new public section | content/read for that section |
| Post comments | content/create for the comment class, limited to the places that take comments |
| Search | nothing: search shows what they may read |
| Buy | shop/buy |
| See tag pages | tags/read, tags/view |
| Subscribe to a newsletter | the newsletter module's subscribe policies |
Keep the role small. Each addition is something every visitor on the internet may do.
Testing as a visitor
- Use a private browser window, not your admin session.
- Check a page in each section, a hidden page (must be gone), a members page (must ask to log in) and a draft (must be invisible).
- The access check console command shows what a user may do: see
doc/eng-us/examples/commands/accesscheck.mdwhen the examples are installed, or the role pages in the administration.
Common mistakes
| Mistake | Effect |
|---|---|
content/read without a section limitation | visitors can open user accounts and setup objects |
| A new section forgotten in the Anonymous role | its pages give "access denied" to everyone |
| Media in a section visitors may not read | images in articles still show (served as files), but media pages do not |
RequireUserLogin=true copied to the public siteaccess | everyone is sent to the login page |
Related pages
- Member registration and members-only areas
- Sections and object states for site builders
- Security and audit
- Free documentation: this page is free to copy, translate and improve under the GNU FDL 1.3.
Become an Exponential Partner
Partners share their information, provide funding, contribute back and develop the products with us, and that is how Exponential grows. A partner website and dashboard are planned for mid-2027: please become a partner today to speed up our growth rate and land new features faster.